The compliance landscape continues to evolve rapidly, with regulators increasing their focus on governance, operational resilience, consumer outcomes and risk management. While many AFSL holders have invested significant resources in their compliance frameworks, audits, reviews, and remediation activities continue to identify recurring weaknesses that often go unnoticed until an incident, complaint, or regulatory review occurs.
The challenge is that these weaknesses rarely arise because a policy does not exist. More often, they emerge because frameworks have not evolved as businesses have grown, technology has changed, or regulatory expectations have shifted. Based on the issues currently being discussed across the industry and common themes emerging through compliance reviews, several blind spots continue to appear across financial services businesses.
One of the most common issues is governance frameworks that no longer reflect how the business operates. Policies, committee structures and reporting lines may have been appropriate several years ago. Still, many organisations have expanded their service offerings, increased representative numbers, adopted new technology or introduced outsourced providers without reviewing whether governance arrangements remain fit for purpose. This can create gaps in accountability and oversight that become increasingly difficult to identify as businesses grow.
Another emerging blind spot is adopting artificial intelligence without appropriate governance controls. AI tools are becoming increasingly common across business operations, marketing, client communications and administration functions. While the efficiency benefits are significant, many businesses have not yet formally considered issues such as data security, privacy, content approval, record-keeping, or oversight responsibilities. As regulators continue to focus on technology governance and operational resilience, businesses may need to demonstrate greater oversight of how AI is used within their organisations.
Website governance is also becoming increasingly important. Many businesses regularly review internal policies and procedures but rarely apply the same discipline to website content, service descriptions, adviser profiles and client-facing information. As AI-assisted search tools become more prevalent, inaccurate or outdated website information can create both compliance and reputational risks. Businesses are increasingly judged not only on their documented compliance framework but also on the information publicly available about their services and operations.
AML/CTF frameworks are another area where businesses often assume greater maturity than they actually have. While many organisations maintain the required policies, procedures, and risk assessments, fewer regularly test whether controls operate effectively. Recent discussions around debanking and rising AML expectations reinforce the importance of showing that frameworks are actively monitored, reviewed, and implemented in practice rather than existing solely as documentation.
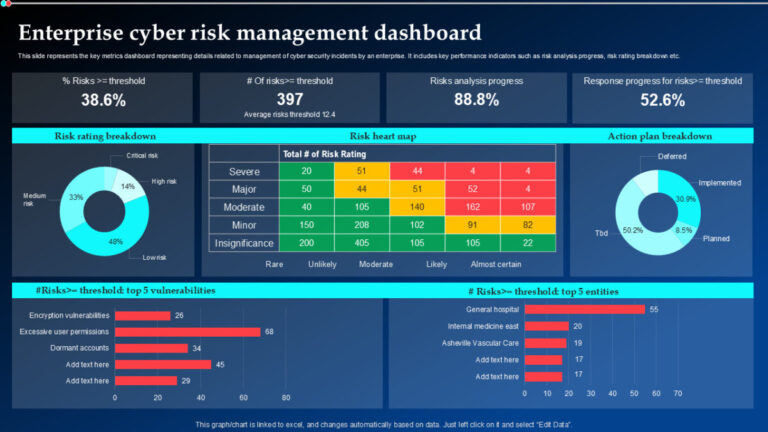
Finally, many businesses remain focused on historical risks while emerging threats continue to evolve. Deepfake fraud, AI-generated scams, cybersecurity threats, digital assets and third-party service provider risks are becoming increasingly relevant across financial services. Organisations that do not regularly review their risk registers and governance frameworks may find that emerging risks are not being appropriately identified, assessed or monitored until a significant event occurs.²
A common theme across these blind spots is that they are often difficult to identify from within the business. Internal teams naturally become familiar with existing processes and controls, making it challenging to recognise where gaps may have developed over time. Independent reviews provide an opportunity to assess whether governance frameworks, compliance arrangements and operational controls remain aligned with both current business practices and evolving regulatory expectations.
Call to Action
A simple question every AFSL holder should consider is:
If an independent reviewer assessed your business tomorrow, what compliance blind spots would they identify first?
Many organisations have strong compliance frameworks on paper but have never independently tested whether governance arrangements, risk management processes, monitoring activities and operational controls remain effective as the business evolves.
AICS conducts independent AFSL Licence Reviews, Governance Reviews and Compliance Health Checks that identify gaps before they become complaints, breaches, remediation activities or regulatory concerns. Our reviews assess governance structures, compliance frameworks, operational controls and emerging risks to provide practical recommendations that strengthen both compliance outcomes and business resilience.
If you would like an independent assessment of your compliance framework, governance arrangements or operational controls, contact Cheyenne and the team to discuss your business at [email protected] or call 07 3251 2481.
References